Commercial Security Camera Systems: Coverage Guide
Plan commercial security camera systems for coverage, retention, and useful alerts across sites, without buying cameras as isolated hardware.
CONTINUE READINGIT Procurement Services: Reduce Vendor Complexity
Build an IT procurement process that connects business needs, architecture, risk, and lifecycle ownership while reducing avoidable vendor complexity.
CONTINUE READINGCloud Security Consulting: A Decision Framework for Teams
Learn how to evaluate cloud security consulting for hybrid environments, compare engagement models, prioritize controls, and build accountable outcomes.
CONTINUE READINGCybersecurity Strategy Consulting: A Practical Roadmap
Learn how cybersecurity strategy consulting turns risk priorities into sequenced work, accountable owners, measurable outcomes, and a durable operating plan.
CONTINUE READINGSoftware Supply Chain Security: A Practical Risk Management Guide
Learn how to assess software supply chain security, prioritize supplier and build risks, and create controls your IT and security teams can sustain.
CONTINUE READINGMDR vs. EDR: Choosing the Right Detection and Response Model
Compare MDR and EDR by ownership, response, staffing, and operational fit. Use this guide to define the right detection model for your IT team.
CONTINUE READINGCloud Access Security Broker: A Practical Guide for IT Leaders
Learn how a cloud access security broker works, where it fits in your security architecture, and how to assess coverage, controls, operations, and provider fit.
CONTINUE READINGPurple Team Security Assessment: Turning Attack Simulation Into Better Defenses
Learn how a purple team security assessment aligns offensive testing with defensive response, what to include in scope, and how to turn findings into action.
CONTINUE READINGAttack Surface Management: A Decision Guide for IT Leaders
Learn how IT leaders can scope, prioritize, and operationalize attack surface management across cloud, endpoints, identities, suppliers, and critical services.
CONTINUE READING
Critical Infrastructure Cybersecurity: A Practical Guide for IT Leaders
A practical framework for assessing critical infrastructure cyber risk, prioritizing safeguards, and coordinating IT, OT, vendors, and response teams.
CONTINUE READINGEnterprise Architecture Consulting: A Practical Guide for IT Leaders
See how enterprise architecture consulting aligns applications, data, infrastructure, security, and operating models with business goals.
CONTINUE READINGPhysical Security Risk Assessment: A Practical Guide for IT Leaders
Learn how IT leaders can assess facility, people, and technology risks, prioritize safeguards, document evidence, and build a practical improvement plan.
CONTINUE READINGHybrid Cloud Data Governance: A Practical Guide for IT Leaders
Build a practical hybrid cloud data governance model: assign ownership, classify data, control access, and keep policies consistent across environments.
CONTINUE READINGAWS Cloud Governance for Regulated Companies: A Practical Guide
AWS cloud governance for regulated companies is not a policy document that sits apart from engineering. It is the operating model for deciding who can create and change cloud resources, which safeguards apply by default, how exceptions are approved, and what evidence demonstrates that controls are working. For CIOs, CISOs, and IT directors, the goal is to make compliance and resilience part of ordinary delivery rather than a last-minute audit exercise.
CONTINUE READINGIT Support for Internal IT Departments
Learn how internal IT teams can structure escalation paths, improve handoffs, and coordinate outside support without losing ownership or context.
CONTINUE READINGImportance of Regular Security Risk Assessments
Learn why recurring security risk assessments matter, how to set a useful cadence, and how to turn findings into prioritized, measurable risk reduction.
CONTINUE READINGHow to Upgrade Office Network Cabling
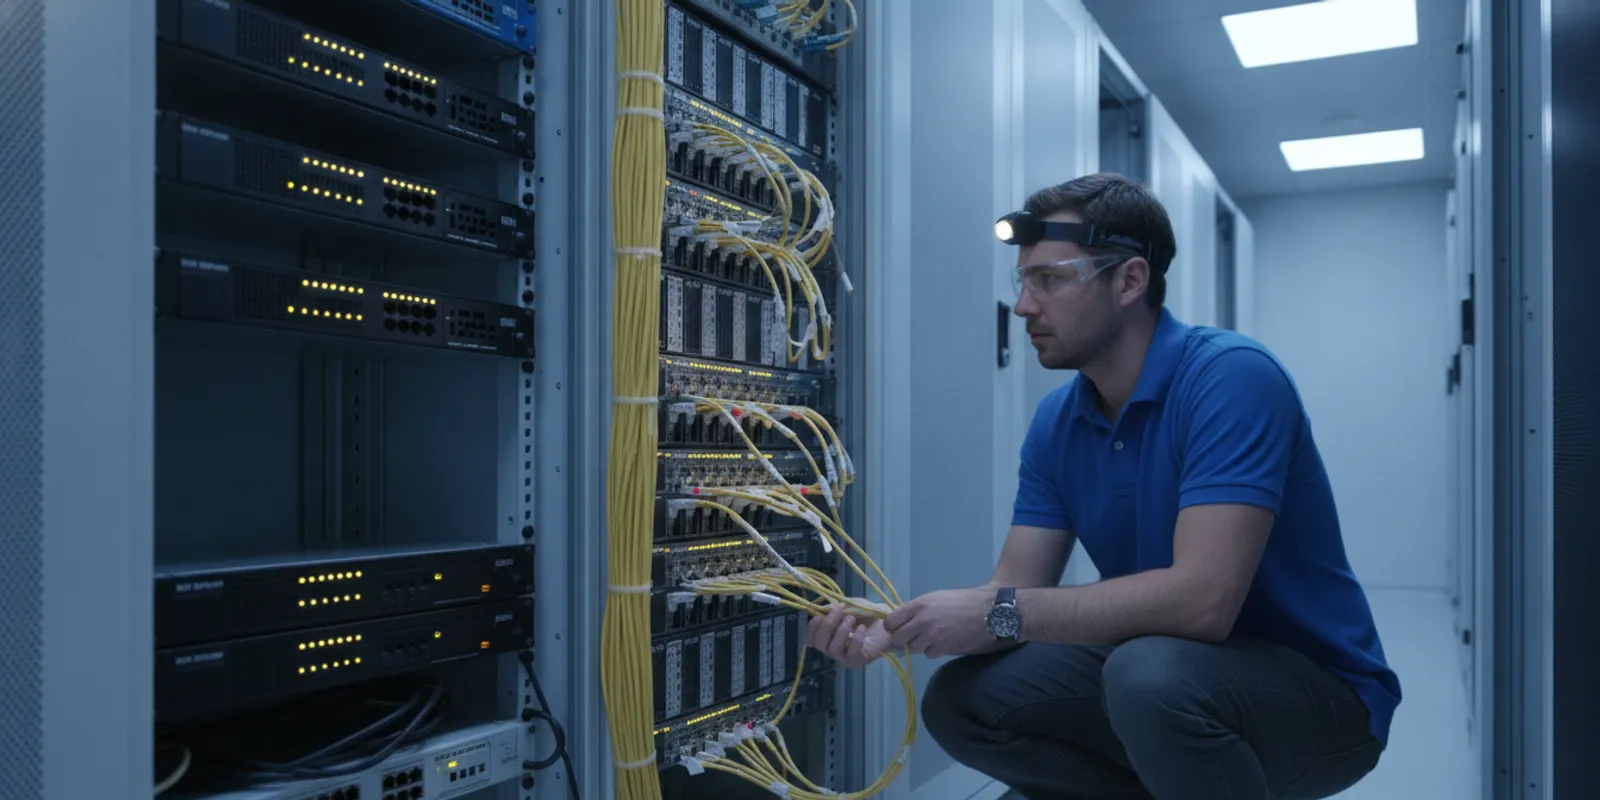
Knowing how to upgrade office network cabling starts with defining the business need. A refresh may address unreliable connections, capacity requirements, new wireless access points, an office move, or an aging physical layer. The goal is not simply to install new cable. It is to deliver a tested, documented network foundation without avoidable service disruption.
CONTINUE READINGCloud Access Security Broker (CASB) for 21 CFR Part 11
Cloud access security broker (CASB) controls can help regulated organizations govern how users, devices, applications, and data interact across cloud services. For life sciences IT, quality, and compliance leaders, the relevant question is not whether a CASB makes a platform compliant. It is how CASB visibility, policy enforcement, data protection, and audit evidence fit into the risk-based control model for electronic records and signatures. This guide connects CASB capabilities with 21 CFR Part 11 scope, validation, shared responsibility, and ongoing operations.
CONTINUE READINGFDA Cybersecurity Guidance: An IT Readiness Framework for Life Sciences
Apply FDA cybersecurity guidance to life sciences IT with practical steps for scope, risk, response, supplier oversight, and evidence.
CONTINUE READINGMedical Device Cybersecurity: Managing Risk Across the Product Lifecycle
See how IT and security leaders can govern medical device risk from design and procurement through deployment, maintenance, and retirement.
CONTINUE READING