Cloud Access Security Broker: A Practical Guide for IT Leaders
Learn how a cloud access security broker works, where it fits in your security architecture, and how to assess coverage, controls, operations, and provider fit.
CONTINUE READINGPurple Team Security Assessment: Turning Attack Simulation Into Better Defenses
Learn how a purple team security assessment aligns offensive testing with defensive response, what to include in scope, and how to turn findings into action.
CONTINUE READINGAttack Surface Management: A Decision Guide for IT Leaders
Learn how IT leaders can scope, prioritize, and operationalize attack surface management across cloud, endpoints, identities, suppliers, and critical services.
CONTINUE READING
Critical Infrastructure Cybersecurity: A Practical Guide for IT Leaders
A practical framework for assessing critical infrastructure cyber risk, prioritizing safeguards, and coordinating IT, OT, vendors, and response teams.
CONTINUE READINGEnterprise Architecture Consulting: A Practical Guide for IT Leaders
See how enterprise architecture consulting aligns applications, data, infrastructure, security, and operating models with business goals.
CONTINUE READINGPhysical Security Risk Assessment: A Practical Guide for IT Leaders
Learn how IT leaders can assess facility, people, and technology risks, prioritize safeguards, document evidence, and build a practical improvement plan.
CONTINUE READINGHybrid Cloud Data Governance: A Practical Guide for IT Leaders
Build a practical hybrid cloud data governance model: assign ownership, classify data, control access, and keep policies consistent across environments.
CONTINUE READINGAWS Cloud Governance for Regulated Companies: A Practical Guide
AWS cloud governance for regulated companies is not a policy document that sits apart from engineering. It is the operating model for deciding who can create and change cloud resources, which safeguards apply by default, how exceptions are approved, and what evidence demonstrates that controls are working. For CIOs, CISOs, and IT directors, the goal is to make compliance and resilience part of ordinary delivery rather than a last-minute audit exercise.
CONTINUE READINGIT Support for Internal IT Departments
Learn how internal IT teams can structure escalation paths, improve handoffs, and coordinate outside support without losing ownership or context.
CONTINUE READINGImportance of Regular Security Risk Assessments
Learn why recurring security risk assessments matter, how to set a useful cadence, and how to turn findings into prioritized, measurable risk reduction.
CONTINUE READINGHow to Upgrade Office Network Cabling
Knowing how to upgrade office network cabling starts with defining the business need. A refresh may address unreliable connections, capacity requirements, new wireless access points, an office move, or an aging physical layer. The goal is not simply to install new cable. It is to deliver a tested, documented network foundation without avoidable service disruption.
CONTINUE READING21 CFR Part 11 IT Controls for Regulated Teams
Learn how life sciences teams operationalize 21 CFR Part 11 through risk-based controls for records, signatures, access, and change.
CONTINUE READINGFDA Cybersecurity Guidance: An IT Readiness Framework for Life Sciences
Apply FDA cybersecurity guidance to life sciences IT with practical steps for scope, risk, response, supplier oversight, and evidence.
CONTINUE READINGMedical Device Cybersecurity: Managing Risk Across the Product Lifecycle
See how IT and security leaders can govern medical device risk from design and procurement through deployment, maintenance, and retirement.
CONTINUE READINGVisitor Management System Governance Guide
Govern a visitor management system across regulated sites. Set policy, control site exceptions, and keep contractor access audit-ready before review today.
CONTINUE READINGManaged SIEM: What to Evaluate Beyond Log Collection
Evaluate managed SIEM beyond log ingestion with practical criteria for coverage, detection quality, response ownership, integrations, and governance.
CONTINUE READINGWhat Is Endpoint Security? A Decision Guide
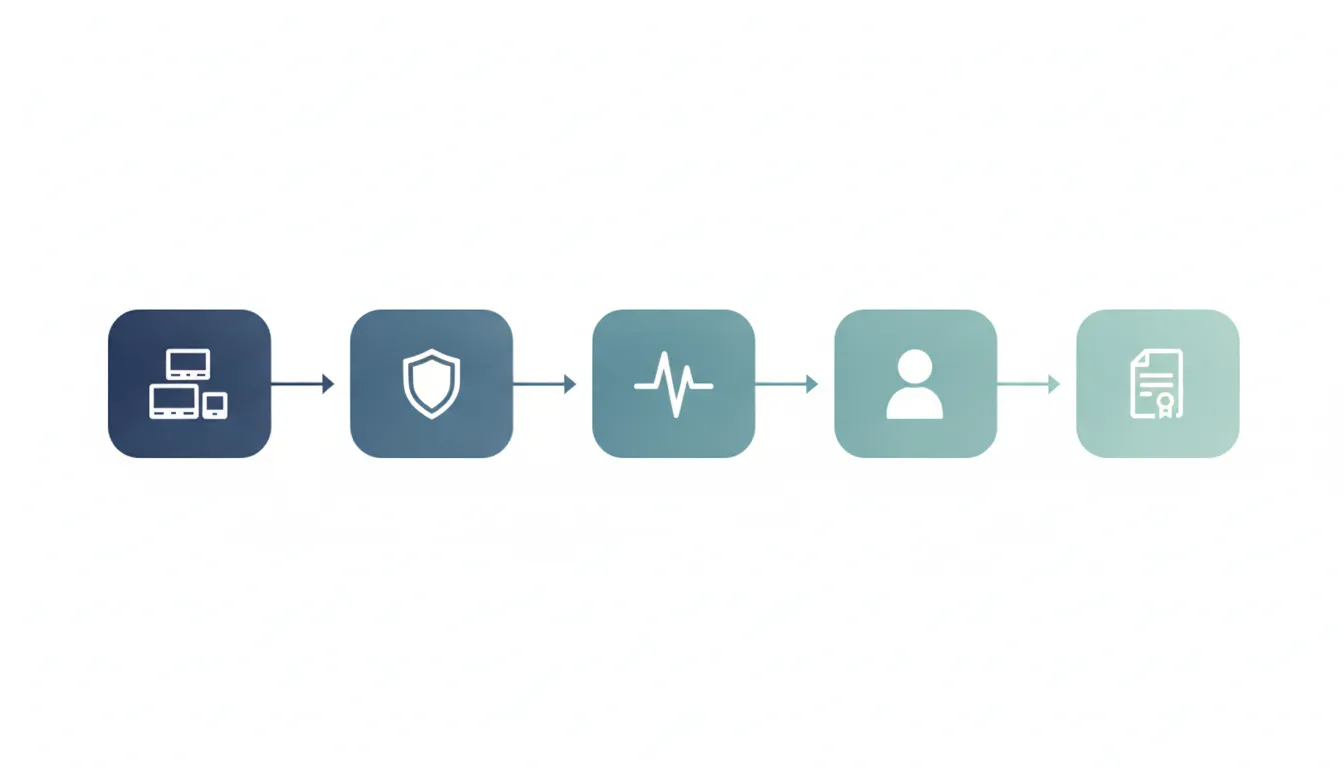
What is endpoint security for a mature IT team? Use five questions to decide if current controls are enough, or if response help is due.
CONTINUE READINGCommercial Security Systems: A Unified Cloud-Managed Guide
Design commercial security systems for multiple sites with a practical framework for video, access, identity, alerting, and data governance.
CONTINUE READINGAWS Security Best Practices for Regulated Mid-Market Enterprises
Learn AWS Security Best Practices for regulated mid-market firms in life sciences, biotech, and finance, with practical controls for audits and secure growth.
CONTINUE READINGCyber Liability Insurance: What Mid-Market IT Leaders Should Evaluate
Learn how to assess cyber liability insurance limits, exclusions, controls, and incident response readiness before renewal or a major technology change.
CONTINUE READING